Indirect Prompt Injection: When the Poison Comes From Outside
Your agent doesn't need to be attacked directly. It's enough to poison a website, a ticket or an email that it will consume automatically.
Your agent doesn't need to be attacked directly. It's enough to poison a website, a ticket or an email that it will consume automatically.
A poisoned README can make your agent exfiltrate secrets. We build a lab to prove it and learn how to defend ourselves.
A common scenario in teams managing Azure infrastructure with IaC: the Windows systems team opens a ticket requesting disk changes on a VM.
You receive a cost-optimization ticket. A classic scenario: an AKS with 3 nodes, only 2 real application pods, CPU at 8% and memory at 12%,

We build an agent in Dify that receives natural-language specifications and automatically deploys VMs via a FastAPI + Vagrant API
Most Linux distributions follow a default-permit model: everything is allowed until the administrator restricts it. This post inverts that m
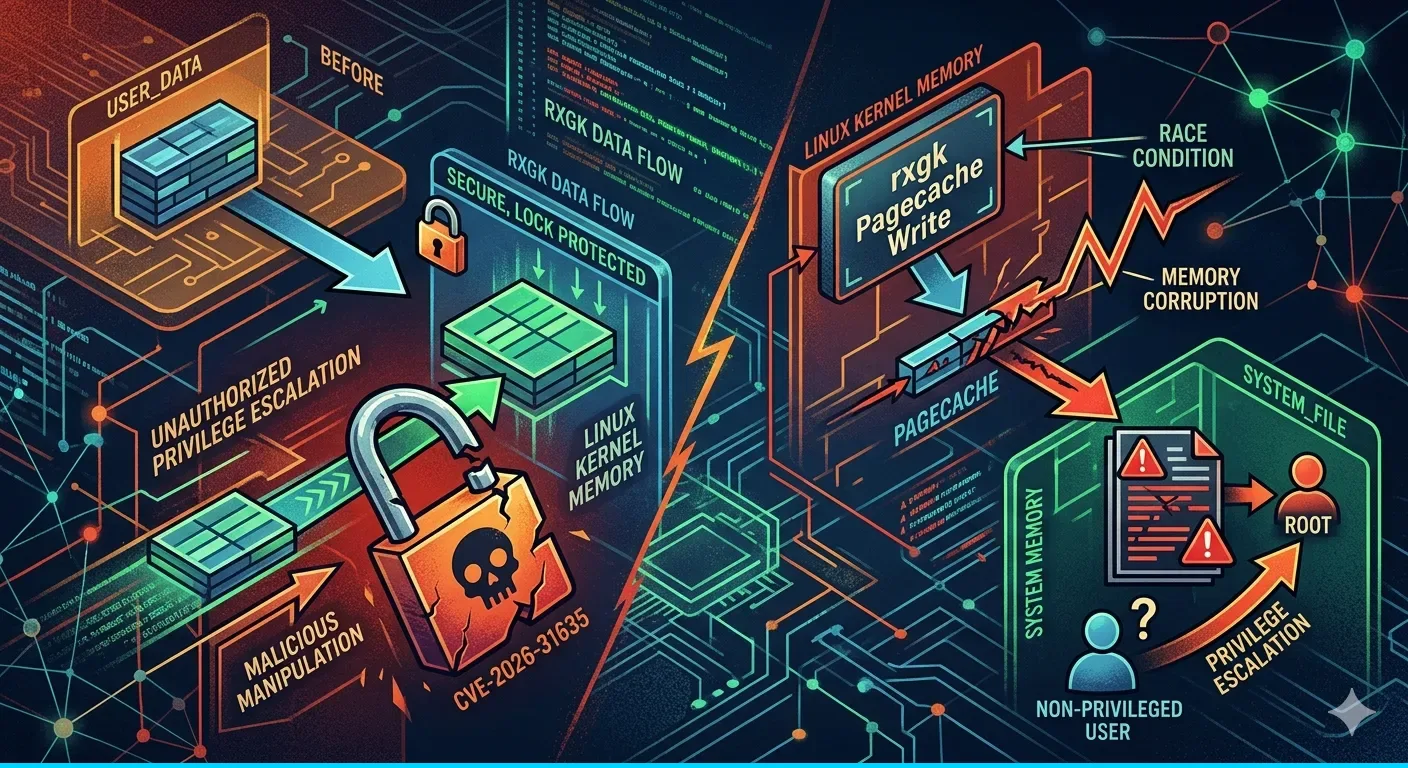
"What is DirtyDecrypt? DirtyDecrypt (also known as DirtyCBC) is a local privilege escalation vulnerability in the Linux kernel that allows a
"CVE-2026-7270 is a local privilege escalation vulnerability in the FreeBSD kernel that allows an unprivileged user to gain root on systems
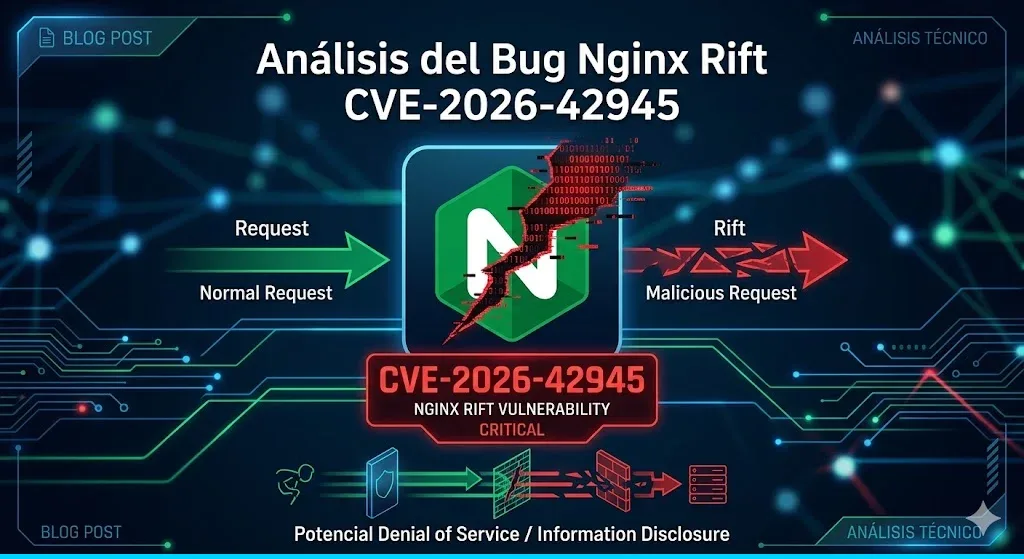
What is Nginx Rift (CVE-2026-42945)
What is Fragnesia (CVE-2026-46300)
What is ssh-keysign-pwn (CVE-2026-46333)
What is Dirty Frag (CVE-2026-43284 + CVE-2026-43500)